Context
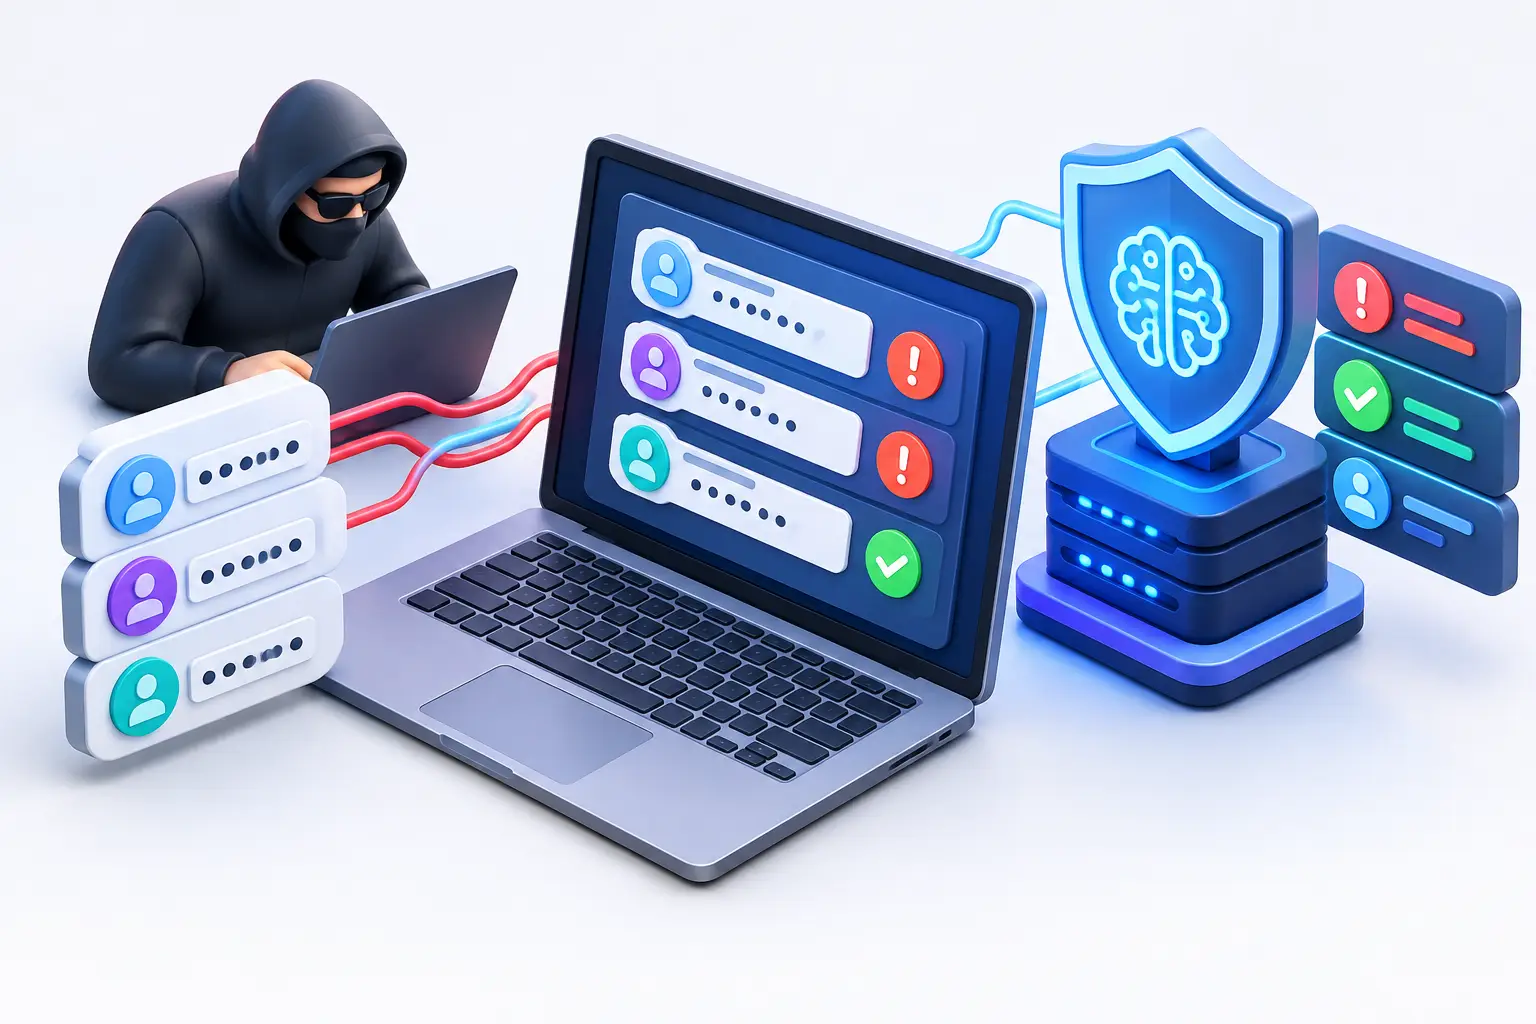
A login can succeed with the correct password and still belong to an attacker. Credential stuffing exploits passwords reused across services: credentials exposed elsewhere are tested against your customers' accounts.
For a commerce platform, the damage may appear after authentication as stolen loyalty value, unauthorized orders, or changes to customer details. Protecting the login endpoint is essential. Understanding the attempts that led to a successful session, and the actions that follow it, makes the response more useful.
Table of contents
What is credential stuffing?
Credential stuffing tests username and password pairs obtained from another breach. It differs from password spraying, which tries a small set of common passwords across many accounts, and password guessing directed at one account. OWASP's prevention guidance distinguishes these attack patterns.
Reused credentials are the opportunity. An operation may distribute attempts across networks and sessions, so a limit on one IP address can miss the wider activity. Some attempts fail; the successful ones require attention too.
A spike in failed logins is useful evidence, but it can also follow an outage or a change to the login experience. Investigate the account distribution, request sequences, and authentication outcomes before attributing the spike to an attack.
Map every route that can authenticate a customer
Inventory browser login, mobile authentication, direct API routes, account recovery, and any alternative purchase flow that signs a customer in. Identify which component verifies credentials and where each protective check is enforced.
Confirm that the server applies the intended controls to every supported path. A challenge on the visible login page does little for a direct request to an endpoint that accepts the same credentials without that check.
Include password-reset and verification flows in the review. They have different rules from login, but an operation can shift towards them when the primary route becomes harder to use. Give each route an owner and a defined response to excessive activity.
Look for a campaign across accounts and sessions
Build the investigation from the pattern rather than the appearance of one request. Useful questions include:
- Is a device or session attempting many unrelated accounts?
- Do repeated failures lead immediately to another identity through the same request sequence?
- Does similar activity continue through changing network routes?
- Are accounts returning after an earlier restriction through related sessions?
- Do successful logins lead to unusual changes or use of stored value?
Combine these findings with account history and service conditions. A password manager can fill a form quickly. A customer can switch devices, travel, or use a privacy tool. A browser that looks modern or an IP address that looks residential also does not establish that the request is legitimate.
Make the evidence available to both security and fraud teams. The login sequence and the later redemption may be parts of one case, even when separate systems recorded them.
Strengthen authentication alongside detection
Use multi-factor authentication for the accounts and actions that need it, and offer passkeys where your identity system supports them. Test fallback and recovery paths as carefully as the primary login route. An alternate path should not quietly undermine the protection you intended.
OWASP identifies MFA as a central defense against reused-password attacks. Detection remains useful for identifying campaigns and choosing when additional verification is appropriate.
Review breached-password checks when customers create or change a password. Give customers a usable recovery process and clear guidance when you establish that an account needs protection. A login policy that nobody can complete will generate workarounds and support demand.
Set limits that protect accounts and availability
Choose request budgets and observation windows from your authentication capacity and normal usage. Review both repeated attempts against one account and coordinated attempts across many accounts. Keep account, route, and campaign context alongside network limits.
OWASP's authentication guidance recommends associating failed-login counters with the account. It also warns that an attacker can exploit lockout to deny the legitimate customer access. Evaluate throttling, temporary restrictions, and verification against that risk.
Make retries predictable after a connection error. Test the effect of a shared network, a release-day traffic spike, and a recovering authentication service. Limits that were reasonable on an ordinary day may interrupt customers during a popular launch.
Continue protection after a successful login
A correct password establishes that the secret matched. It does not erase a suspicious sequence that preceded the login. Review the session in context before allowing sensitive changes or use of valuable account features.
Decide where fresh verification is appropriate, such as changes to credentials or recovery details. OWASP's session-management guidance recommends reauthentication after high-risk events and server-side session invalidation when a session is ended.
For a confirmed compromise, follow a defined recovery process: contain the affected sessions, help the customer regain control, and review related changes or transactions. Record which actions need reversal and which team owns each decision. Blocking the next login attempt alone does not repair an already compromised account.
Evaluate credential stuffing detection tools on your flows
Ask a provider to demonstrate the accounts and sessions behind a detection, the endpoints covered, and the response applied. Your team needs an explanation it can investigate and tune.
Evaluate realistic cases: distributed attempts, changing devices, returning customers after password resets, legitimate shared networks, and suspicious activity that includes a successful login. Use your actual identity provider and supported API paths in the assessment.
Kairal's COMPOSITE® technology connects activity across devices, accounts, and visits to support investigations. Use that context with authentication outcomes and the policies enforced by your identity system.
Establish what happens when a protection component becomes unavailable. Agree on the response with engineering and operations before an incident, then test how the configuration affects login availability and customer support.
Measure account safety and legitimate access
Review confirmed compromised accounts, successful protected logins, verification completion, recovery turnaround, support appeals, and the time needed to understand a campaign. Keep attempted abuse separate from confirmed account takeover.
Do not label every failed login as a prevented compromise. The password may have been wrong, the account may not exist, or the request may have come from a customer. Likewise, a fall in alert volume may reflect changed attacker behavior rather than a complete end to the campaign.
Compare outcomes before and after policy changes while accounting for outages and traffic shifts. Your goal is a login journey that resists repeated credential testing and remains usable for customers.
To review how suspicious login activity connects to account abuse, discuss your customer journey with Kairal. Bring the authentication routes, the actions available after login, and the evidence your teams currently review separately.